scrolling text

Selamat datang ke blog HackingSoftware41. Selamat membaca. Jangan lupa lawati www.jomgegar.com jumpa anda disana

ads

loading...

Wednesday, November 27, 2013

Uji Tahap Keselamatan Pelayar anda secara percuma / Test your security level of your browser for free


Assalamualaikum kawan-kawan semua, entry kali ini aku nak cakap pasal keselamtan browser anda. Adakah browser anda berada pada tahap yang selamat? Jika anda menggunakan "outdate software" akan menyebabkan browser anda berada pada tahap yang lemah dan mampu di eksploit oleh sesapa sahaja. Apabila penggodam dapat identify kelemahan yang ada pada browser anda, maka penggodam mempunyai cara tertentu untuk mengeksploit browser anda.Senang crita ada "vulnerability" kat browser korang tu. Oleh itu, aku cadangkan pengguna browser tak kira lah brand apa untuk scan tahap keselamatan yang terdapat pada browser anda itu. Untuk scan, anda pergi ke page ini >


Setelah anda berada di page tersebut, korang bolehlah klik "browser scan" dan korang kena tunggu beberapa minit dan korang akan dapat keputusan scanning tersebut. Lihat seperti gambar kat bawah ni.


Selepas dah keluar keputusan seperti gambar kat atas ni, korang bolehlah buat step seterusnya untuk update plugin yang "outdate" tu. Hanya perlu klik "download Now" dan teruskan step untuk install latest plugin.


Selepas korang dah update semua plugin tu, korang bolehlah scan sekali lagi untuk tengok tahap keselamatan browser korang. Lagi satu, window korang mesti kena enable update, kalau tak, penggoadam akan senyum je la bila dia scan PC korang atau laptop korang banyak "vulnerablity" huhu...


Monday, November 18, 2013

[Free Download] Havij Version 1.16 | SQL Injection Tool

JANGAN DISALAHGUNAKAN, KAMI TIDAK AKAN BERTANGGUNGJAWAB DIATAS SESUATU YANG BERLAKU, SEKADAR UNTUK BERKONGSI SAHAJA


Description :

Havij is an automated SQL Injection tool that helps penetration testers to find and exploit SQL Injection vulnerabilities on a web page.


It can take advantage of a vulnerable web application. By using this software user can perform back-end database fingerprint, retrieve DBMS users and  password hashes, dump tables and columns, fetching data from the database, running SQL  statements and even accessing the underlying file system and executing commands on the  operating system.


The power of Havij that makes it different from similar tools is its injection methods. The success rate is more than 95% at injectiong vulnerable targets using Havij.


The user friendly GUI (Graphical User Interface) of Havij and automated settings and detections makes it easy to use for everyone even amateur users.


What's New?


  • Multithreading
  • Oracle Blind injection method.
  • Automatic all parameter scan added.
  • New blind injection method (no more ? char.)
  • Retry for blind injection.
  • A new method for tables/columns extraction in mssql blind.
  • A WAF bypass method for mysql blind.
  • Getting tables and columns even when can not get current database.
  • Auto save log.
  • bugfix: url encode bug fixed.
  • bugfix: trying time based methods when mssql error based and union based fail.
  • bugfix: clicking get columns would delete all tables.
  • bugfix: reseting time based method delay when applying settings.
  • bugfix: Oracle and PostgreSQL detection 

By Bola Getah

Friday, November 15, 2013

[TuT] how to Run Man in The Middle Attack in your local area network / Cara-cara bagaimana nak setup serangan Man in The Middle dalam rangkaian kawasan tempatan


Assalamualaikum kawan-kawan..Tutorial kali ini aku nak show you about how to attack as Man in The Middle in your local area network. Ok untuk laksanakan attack ini korang tak perlu risau sebab ia hanya menggunakan simple command line sahaja.

"penyerang membuat sambungan bebas dengan mangsa dan menyampaikan mesej di antara mereka,ini secara tidak langsung akan  menjadikan mereka percaya bahawa mereka bercakap secara langsung antara satu sama lain melalui sambungan persendirian, sedangkan seluruh perbualan dikawal oleh penyerang."


Lets start:-

Open your kali Linux


Log in into your 
account


LO


Taip command ifconfig untuk melihat interface mana yang active. 


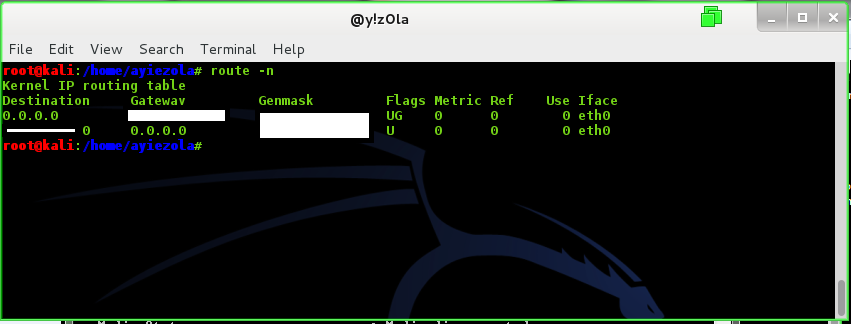
Ok selepas itu kita kena tahu gateway dalam local LAN kita. Taip command route -n untuk melihat gateway tersebut.


Langkah seterusnya adalah Configure Kali Linux korang supaya berfungsi seolah-olah Real Router. Masukkan command seperti dalam gambar rajah diatas.


Type command seperti dalam gambar diatas. Pastikan IP yang di masukkan adalah betul, "capture packet dari target ke router" dan tekan enter


Command line ~ Capture packet diantara router dengan target


Drifnet berfungsi untuk capture all image yang telah di Browse oleh target


Taip command urlsnarf -i eth0 : Urlsnarf berfungsi untuk capture segala url yang lalu-lalang diantara target dan router


" for educational purposes only "


Wednesday, October 30, 2013

[Free Download] VpNium Premium cracked for free / Vpnium Premium percuma untuk download

Assalamualaikum kawan-kawan, entry kali ini aku nak kongsikan dengan korang satu software yang digunakan untuk "stay anonymous" .. Ia menggunakan server dari luar negara. Korang boleh pilih mana-mana server yang kamu minat dan hanya connect sahaja.
copy vpnium.exe dalam "crack folder" dan seterusnya paste pada directory install.
ex: c/program files/vpn > replace vpnium.exe dalam folder ini.


Sunday, October 6, 2013

Laporkan kepada Facebook tentang kematian seseorang pemegang akaun / Special Request for Deceased Person's Account


Assalamualaikum semua kawan-kawan, sahabat yang mengenali diri aku, pembaca blog hackingsoftware41 ni. New entry kali ini aku memang kena buat sebab aku rasa bertanggungjawab terhadap isu ini. "Laporkan kepada Facebook tentang kematian seseorang pemegang akaun / Special Request for Deceased Person's Account" Ramai yang PM aku untuk bantu mereka hack facebook pemegang akaun yang telah meninggal dunia. Untuk pengetahuan kawan-kawan pembaca, sekarang aku tengah sibuk study dan tak ada banyak masa untuk bantu korang solve problem korang ni. Bukan aku tak nak tolong, tapi aku asyik ada class. So entry ni aku nak korang manually report kat facebook tentang niat korang nak deactivate facebook seseorang yang telah meninggal dunia. Cara-cara nya senang sahaja, facebook.com akan respon terhadap request korang.Tambahan pula, kalau request tu datang dari family members lagi bagus.. kita ada cara halal, kita guna cara halal la kan? Tak perlu kita nak hack facebook itu.

Kat bawah ni ada gambar dan video tutorial..


Korang klik kat link ini > http://adf.ly/X9I68 > Isi dan penuhkan segala maklumat yang facebook.com minta.

Another link > http://adf.ly/X9IAF


Harap-harap korang dapat buat yang terbaik untuk family korang. Aku minta maaf atas kesulitan yang berlaku.

Allah Maha Besar..

Thursday, October 3, 2013

[TuT] [Cara-cara nak hack facebook] Dapatkan username & pwd facebook menggunakan teknik pishing dalam kali linux / Get facebook username & password by pishing trick in Kali Linux

JANGAN DISALAHGUNAKAN, KAMI TIDAK AKAN BERTANGGUNGJAWAB DIATAS SESUATU YANG BERLAKU, SEKADAR UNTUK BERKONGSI SAHAJA


Assalamualaikum sahabat-sahabat ku sekalian. Pada entry kali ini aku nak kongsikan dengan kalian semua mengenai satu cara yang kita boleh gunakan untuk dapatkan username dan password seseorang yang kita kehendaki. Tetapi kaedah ini memerlukan kepandaian kita untuk menipu mangsa kita supaya dia terpedaya. Kaedah ini memerlukan kita untuk memperdaya mangsa supaya klik link yang kita bagi kepada mangsa tersebut. Tutorial kali ini memerlukan operating system Kali Linux. Lihat gambar kali linux dibawah ini :


Start :

Ikut step dibawah ini. Sebelum itu sila pastikan anda login Kali Linux anda dahulu. Seterusnya ikut step berikut :


1. then make sure you have login in your Kali Linux, hit commant cd usr/share dan hit enter. Then, enter commant cd set and enter


2. Tengok gambar seperti yang dibawah ni. Hit commant ./set and enter


3. Ok selepas itu, kamu lihat gambar yang dibawah ni, kita akan start kat level 1 tu. social engineering attacks


4. Select 1 then hit enter


5. Select 2 for website attack vector


 6. Select 4 for method tabnabbing attack


7. Select 2 for site cloner (target : www.facebook.com)


8. Put your IP adress on your bottom right .See pic below


8.4. See next step


9. Done with IP adress then put your target in the url to clone


10. You have finish with this. So the next step is get your ip adress and make it not suspicious. ie using url shortner like  url shortner


11. After that copy the given url then send it to your target. I mean your victim. Then send  it with completely suspiciousless.  


12. Picture below show us on the target laptop. After target click the infected link, browser will take a few minutte to generate the pishing site. Victim/target will put username and password on the pishing site.


13. Then see in your screen what happen.


14. The username and password will appear completely.


Kepada sesiapa yang berminat untuk lakukan trick ini, kami tidak bertanggungjawab atas sebarang masalah yang dihadapi oleh attacker. Masalah tanggung sendiri. 

for educational purposes only!!

Wednesday, October 2, 2013

[FreeDownload] VMware 8 with serial key (virtual live machine)

PERKONGSIAN ILMU ADALAH SATU KAEDAH YANG SANGAT BAIK UNTUK KITA SESAMA INSAN. GUNALAH DENGAN CARA YANG HALAL DAN TUJUAN YANG BETUL


Assalamualaikum sahabat pembaca sekalian, pada entry kali ini aku nak berkongsi dengan kalian semua 1 tool yang membolehkan kita install pelbagai iso (image) of OS dalam sebuah laptop. VMWare ver 8 beserta dengan key nya sekali.


How Virtualization Works
The heart of virtualization is the “virtual machine” (VM), a tightly isolated software container with an operating system and application inside. Because each virtual machine is completely separate and independent, many of them can run simultaneously on a single computer. A thin layer of software called a hypervisor decouples the virtual machines from the host and dynamically allocates computing resources to each virtual machine as needed.
This architecture redefines your computing equation and delivers:
Many applications on each server. As each virtual machine encapsulates an entire machine, many applications and operating systems can be run on one host at the same time.
Maximum server utilization, minimum server count. Every physical machine is used to its full capacity, allowing you to significantly reduce costs by deploying fewer servers overall.
Faster, easier application and resource provisioning. As self-contained software files, virtual machines can be manipulated with copy-and-paste ease. This brings unprecedented simplicity, speed and flexibility to IT provisioning and management. virtual machines can even be transferred from one physical server to another while running, via a process known as live migration. You can also virtualize business-critical apps to improve performance, reliability, scalability and reduce costs.

- See more at: https://www.vmware.com/virtualization/virtualization-basics/how-virtualization-works.html#sthash.qMF1p5tI.dpuf


Tapi sebelum install VMWare ni pastikan dahulu laptop anda mempunyai keupayaan yang agak besar. Maksud aku disini adalah RAM , Processor dan HardDisk.


hackingsoftware41


Monday, September 30, 2013

[inFo] Subscribe and get update from your favourite blog/website using sharpReader / Kemaskini blog / website kegemaran anda melalui sharpReader

PERKONGSIAN ILMU ADALAH SATU KAEDAH YANG SANGAT BAIK UNTUK KITA SESAMA INSAN. GUNALAH DENGAN CARA YANG HALAL DAN TUJUAN YANG BETUL.

Assalamualaikum semua sahabat pembaca sekalian. Korang apa khabar? Semoga kalian semua sihat hendaknya. Untuk adik aku > Hisyan > Boleh buat rujukan kat blog cik ni, kalau ada yang tak faham meseg ja terus thru phone. Entry kali ni aku nak kongsikan dengan korang cara-cara nak dapatkan update dari blog-blog kegemaran anda. Senang kata korang dapat update terkini dari blog-blog kegemaran anda tersebut. Aku terpaksa gunakan bahasa baku sebab aku dah set translator dalam blog aku ni supaya ianya dapat pengunjung dari luar negara.

Kamu boleh lihat video di bawah ni untuk lebih faham tentang sharpreader ini.


Tuesday, September 24, 2013

[sHare] md5 gui checksum for windows by toast442.org


There are several functions that are not implemented. Namely, ASCII mode compares. Currently, all checksums are generated in binary mode.

Click Here for an image that shows what the full screen looks like.

The little green circles mean that a file checked out ok. A little red flag means that a file did not match its checksum. A little "NOT" sign means that the file could not be opened.
When generating checksum files, all the icons will be green. Recursion is not yet supported. If files are added from multiple directories, when the checksum file is saved, only the files themselves will be listed; the directories from which they came will not.

To use this thing, choose the action you wish (generate or check) and drag the checksum file (in the case of checking files) or multiple files (for generating checksums). The files that were checked, or for which checksums were generated, will be shown in the list box. To create a file with the contents of the list box in standard md5sum format, either click the Save As.. button or the To Clipboard button. Save As.. of course saves a file directly. To Clipboard copies the same format to the clipboard as text.